Your Basket
09 Sep
Posted By
0 Comment(s)
76 View(s)
A basic printed ID card with a photo, a name and a logo does one job: it lets someone at a glance guess who a person might be. It does very little to stop a determined person faking one, cloning one, or using a stolen card to walk through a door it shouldn't open.
That gap matters more than it used to. Physical security compromises were involved in roughly 9% of breaches captured in IBM's 2025 Cost of a Data Breach Report, and a stranger simply following an employee through a secure door remains one of the most common ways an intruder gets in: 48% of organisations in one survey said they had been compromised by exactly this kind of tailgating, and 66% had experienced some form of physical security breach in the past two years. A card that can be replicated with a laptop and a laminator, or a chip that can be cloned by anyone standing nearby for a few minutes, offers very little resistance against either.
Why "just a card" isn't good enough anymore
Access badges have quietly become one of the most exploitable objects inside most buildings. They're carried openly, worn on lanyards in public, photographed in team pictures, and often left visible on desks. Someone who wants to reproduce one doesn't need much: a phone camera, basic design software, and a laminator can produce a passable fake in an afternoon.
The rise of generative AI has narrowed that gap further. Producing a convincing fake badge used to require a working knowledge of design software and a matching font and colour palette; generative image tools can now approximate a company's logo, layout, and typography from a single prompt.
Against that backdrop, the security features built into a physical card, and the credential technology sitting inside it, are what separate a badge that merely looks official from one that's genuinely difficult to reproduce or misuse.
Visual security features
These are the features you can see, and they're usually the first line of defence because they require specialist print equipment to replicate convincingly.
Holographic overlays. A hologram laminated onto the card shifts colour and pattern depending on the viewing angle, an effect that standard inkjet or laser printers cannot reproduce. It's one of the fastest visual checks a security guard, receptionist or colleague can perform without any equipment: tilt the card, see if the image moves.
UV printing. An additional layer of ink, invisible under normal light and only visible under an ultraviolet lamp, adds a hidden verification step that a casual counterfeiter has no way of anticipating or replicating without knowing it's there.
Subsurface printing with resin coating. Rather than sitting on top of the card, the printed information is protected under a final resin layer, the same lamination principle used on the current UK driving licence. This stops the card being physically altered (scraping off a photo or name and replacing it) without visibly damaging the card.
Embossing and micro-text. Raised lettering or extremely fine printed text that's difficult to replicate at standard print resolution adds another layer that's simple to check by touch or under magnification, but hard for a counterfeiter to match.
Signature panels. A dedicated panel for a handwritten signature gives a second, non-printed reference point that can be compared against a person's actual signature, useful in retail, financial and courier contexts where a card is regularly checked against a signed document.
None of these features are complicated to add, and none of them require replacing your entire card production process. What they do is raise the skill, time and equipment needed to produce a convincing fake to a level well beyond what a phone camera and a laminator can achieve.
Encoded smart cards
Visual features stop casual counterfeiting. They don't stop someone using a genuine-looking but functionally blank card, and they don't stop a legitimate card being cloned electronically. That's where encoded credentials come in.
Magnetic stripe cards were the first widely used encoded format and remain in use for common applications like time and attendance. Whilst best used for applications that hold less data, magnetic stripe cards are still popular across a range of industries.
Low-frequency proximity cards built on magnetic stripe technology by removing the need for physical contact, but the underlying protocol was designed in the 1980s. A simple security feature, the card broadcasts a fixed ID number that any nearby reader can capture and copy.
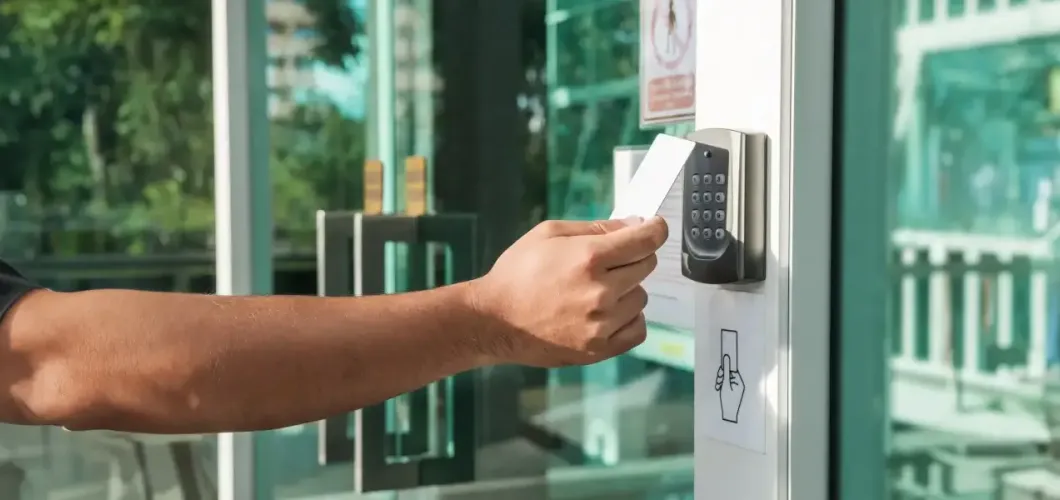
MIFARE Classic became the default upgrade for years and is still one of the most widely deployed access card formats in the world. Its proprietary encryption (Crypto1) has, however, been comprehensively broken by security researchers: a MIFARE Classic card can be cloned in a card-only attack, meaning an attacker only needs a few minutes near the card itself, not the reader, to copy it.
MIFARE DESFire EV2/EV3 and other AES-encrypted smart cards address this directly. These use full AES-128 encryption between card and reader, a standard also used by the US government for classified information, and are, with current computing power, not practically crackable by brute force. If your access control system currently runs on Classic-generation MIFARE, HID Prox, or magnetic stripe, and they protect anything you'd genuinely mind someone accessing, this is the upgrade path that could be most worth prioritising.
Barcodes and QR codes offer a low-cost way to add a unique, scannable identifier without the cost of RFID encoding, useful for attendance tracking, event access or systems where the reader infrastructure already exists.
The right technology depends entirely on what the card is protecting and the system you have in place. A staff badge that only needs to prove identity at a glance has very different requirements from a card that opens a server room or a pharmacy store cupboard.
Process security
Card and credential technology only work if the process around them holds up. Two of the most common failure points aren't the card, they're what happens before and after it's issued.
Verified issuance. A card is only as trustworthy as the process that created it. If anyone can request a replacement over the phone with no verification, or if a photo can simply be slid into a wallet-style holder (as documented in a real 2025 NHS fraud case where three people ran a fraudulent shift-working scheme for months using exactly this method), the strongest hologram in the world doesn't help.
Colour coding. Giving staff, visitors and contractors clearly different card or lanyard colours means an anomaly is visible at a distance, before anyone even needs to read the card. This is one of the simplest and cheapest security features available, and one of the most effective for spotting a problem quickly in a busy environment.
Expiry and revocation. Cards tied to a database that can instantly deactivate a lost, stolen or expired credential close the access gap the moment a loss is reported, rather than leaving a valid credential live until someone remembers to cancel it.
Choosing the right combination for your organisation
Not every organisation needs every feature, and over-specifying security can add unnecessary cost without addressing your actual risk. A rough way to think about it:
- Low-risk environments (small offices, community groups, low-footfall sites): durable PVC construction, clear photo ID and colour-coded lanyards are often sufficient, paired with a verified issuance process.
- Medium-risk environments (schools, healthcare settings, mid-sized offices with restricted areas): add a holographic overlay or UV element and move any access-control cards off legacy magnetic stripe or basic proximity technology.
- Higher-risk environments (facilities handling sensitive data, controlled substances, or high-value equipment): combine visual security features with AES-encrypted smart credentials (MIFARE DESFire or equivalent), tamper-evident lamination, and a database-linked access system that supports instant revocation.
The features covered here aren't exotic. They're widely available, well established, and can typically be added to an existing card programme without starting from scratch. The gap between a card that looks official and one that's genuinely difficult to fake, clone or misuse usually comes down to a handful of deliberate choices: a hologram instead of plain print, AES encryption instead of legacy MIFARE Classic, a verified issuance process instead of a phone request.
Given how cheap and fast it now is to produce a convincing-looking fake, those choices matter more than they used to. Getting them right is one of the most cost-effective security decisions most organisations can make.
Get in touch with the team if you're ready to invest in secure ID Cards.